Financial data, contracts and personal details need traceable protection.
Database in Frankfurt am Main (EU)
The database is hosted in a data centre in Frankfurt am Main, files are also stored in the EU. We follow European standards: GDPR, processing agreements under Art. 28 GDPR and EU standard contractual clauses. All sub-processors are listed openly in the DPA.
GDPR & DPA
The data processing agreement is part of every subscription. You create the full export yourself at any time during your subscription and for at least 90 days after it ends. Deletion follows notice, and retention periods are built in. We back up the database and stored documents every night to separate storage in the EU and delete the backups after 30 days.
Separate agency spaces
The database checks tenant separation and roles on every access, so each agency only sees its own data.
Traceable changes
Changes to documents, approvals and payment operations are logged with time and the person acting.
Controlled shares
External links can be revoked and are time-limited. Only selected data is visible.
Signatures with an audit trail
Every signature is recorded with time, device and a SHA-256 checksum. Later changes become detectable.
In the product
Security you can see in the product.
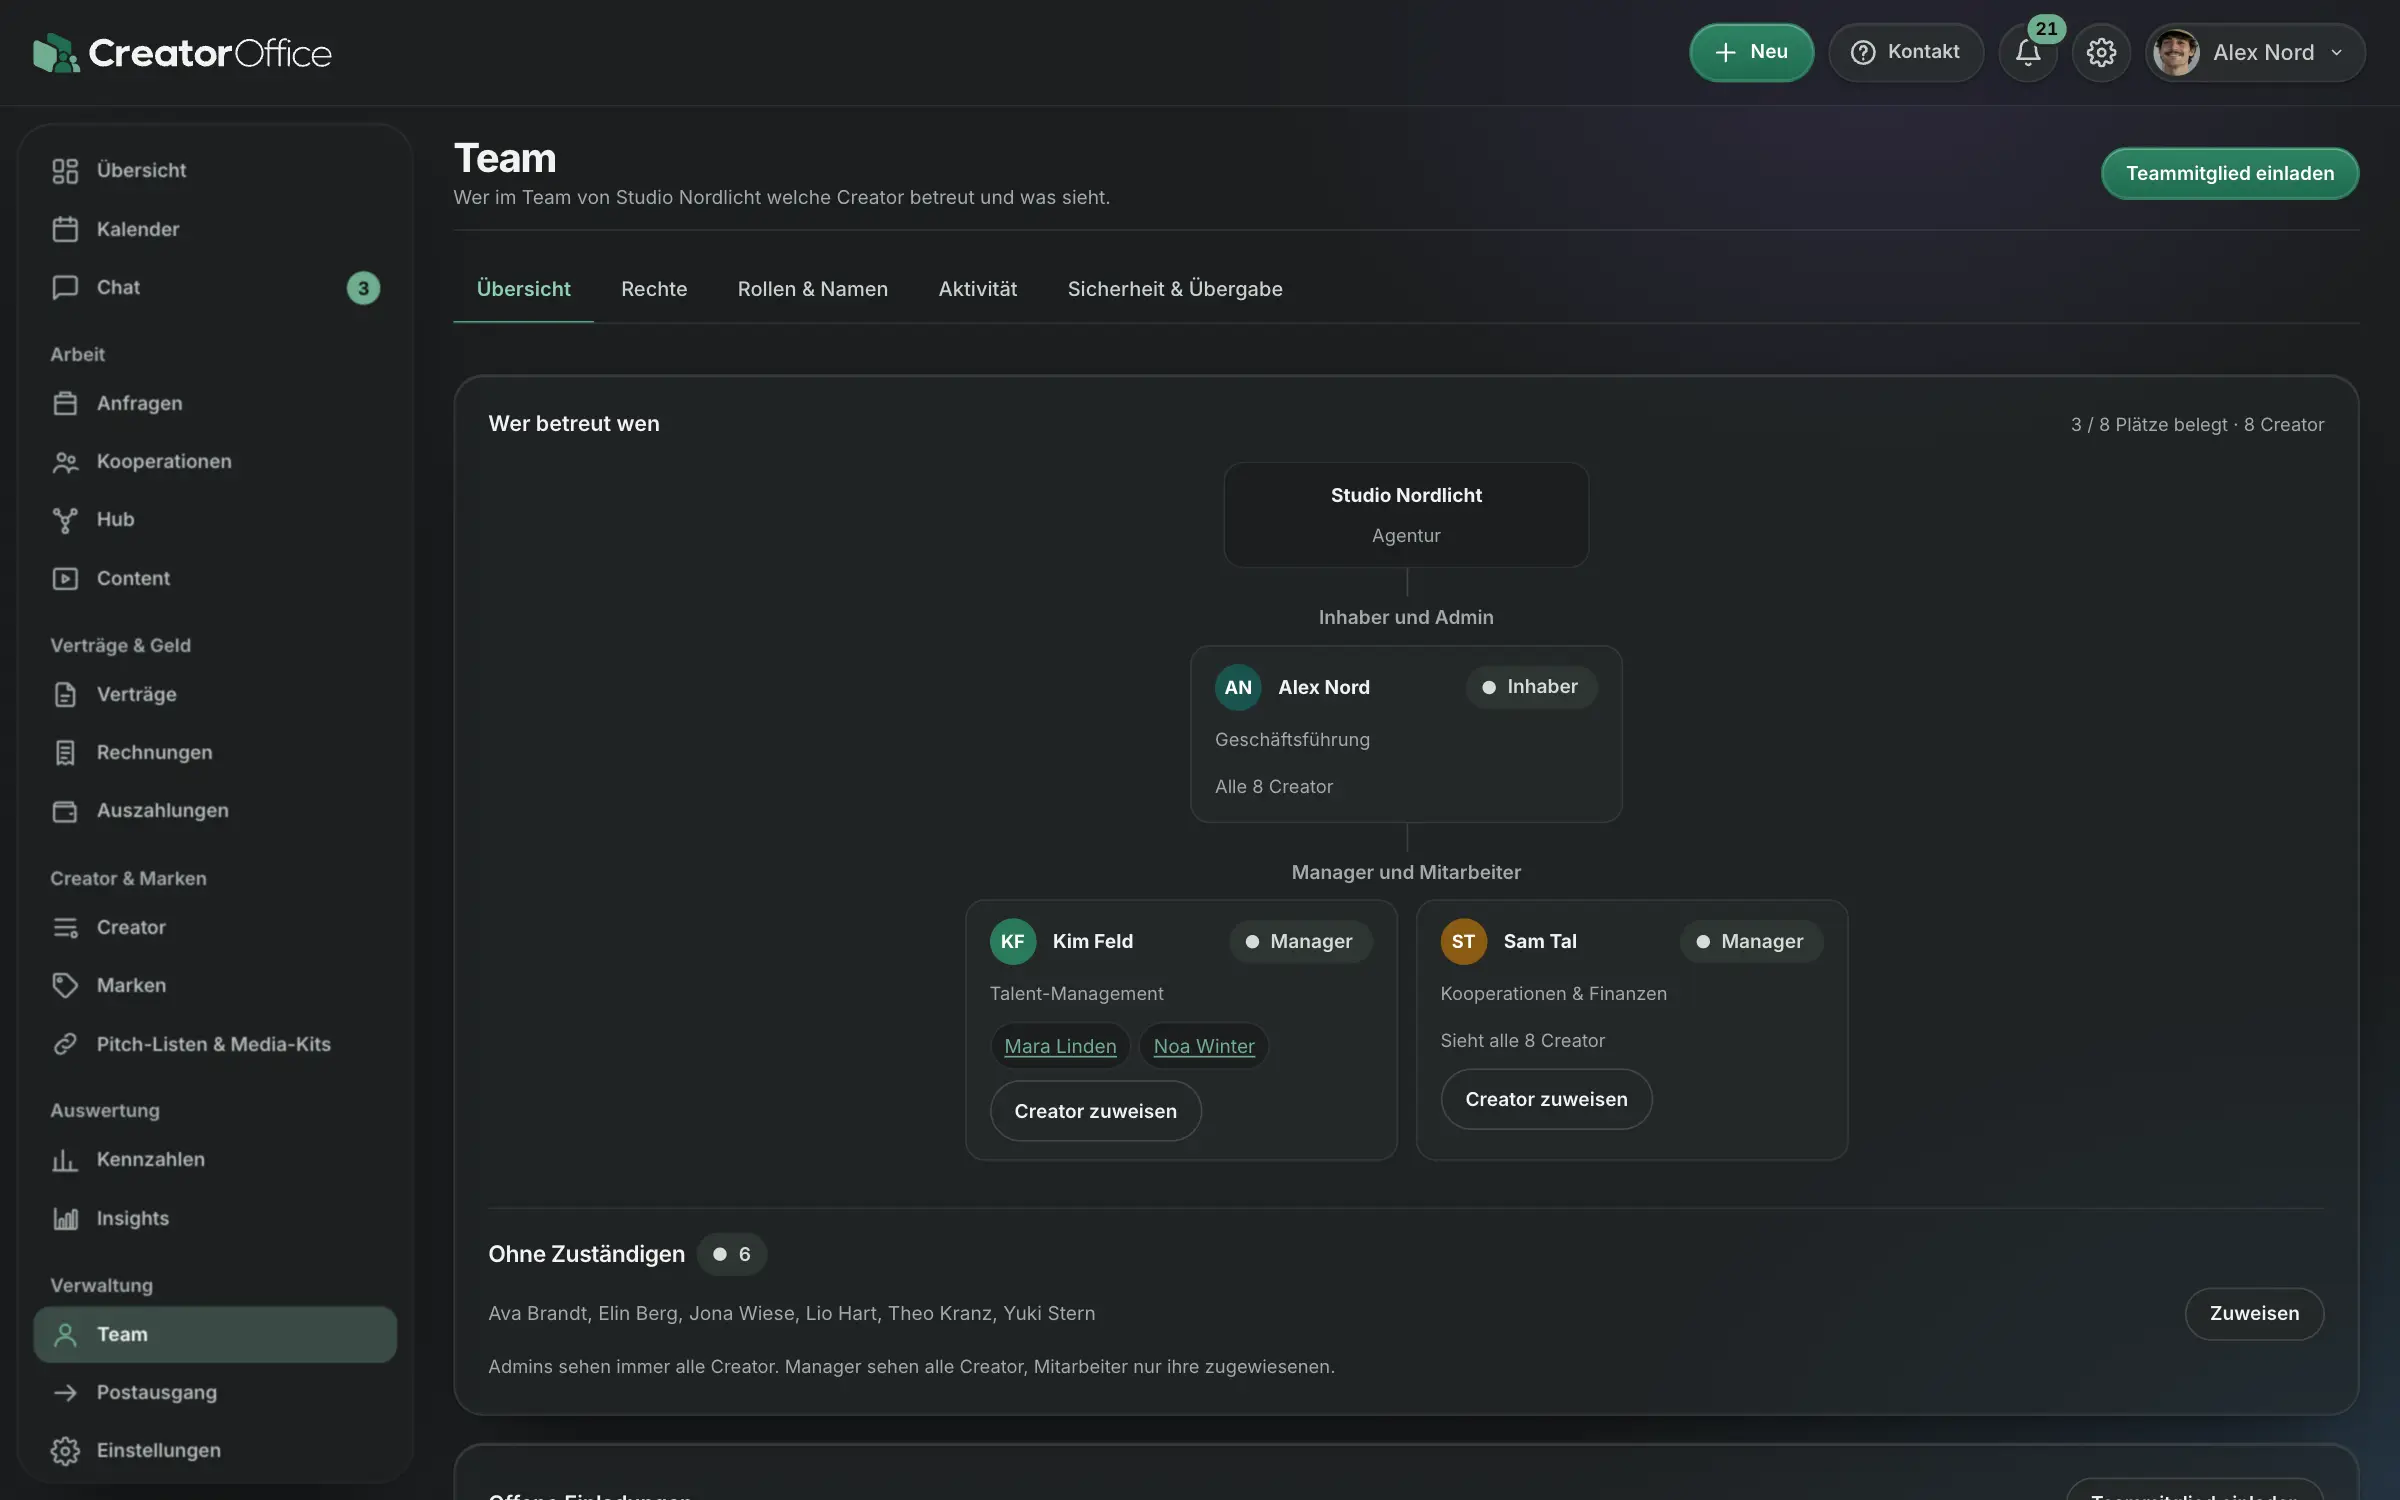
This is how permissions, support access and shares look in the portal.
Permissions in detail
Approve, send dunning notices, make payouts: tick per manager who may do what.
Approve invoices
Send to brand
Send dunning notices
Confirm payments
Make payouts
Countersign contracts
Access is logged
The operator only accesses data where this is needed in the individual case for operation, troubleshooting, maintenance, security or support, including with AI assistance (Claude by Anthropic). Support sessions and AI access are logged, AI replies to customers are only sent after approval, and data is not used to train AI models.
Share data selectively
Brands see a limited view of a single item with a clearly defined sharing scope.